DIVD-2026-00014 - When, not if...
| Our reference | DIVD-2026-00014 |
| Case lead | DIVD Crisis Management Team |
| Author | Various |
| CVE(s) | |
| Status | Open |
| Last modified | 09 Oct 2026 20:01 CEST |
Summary
DIVD got hacked through AI agents and is currently investigating the breach. Incident investigation is ongoing.
What we know sofar
On 21 Sept 2026, a malicious actor managed to breach the Zammad instance that serves as our tickets system for communication with csirt@divd.nl and all other email addresses that end in @csirt.divd.nl. They breached the system using two zero-day vulnerabilities ( CVE-2026-102489 and CVE-2026-102490 ), which we have since reported to Zammad via case DIVD-2026-00015. Zammad has fixed both vulnerabilities the first in release 7.2 and the second in release 7.2.2.
After elevating to root on the system, the actor used AI agents for the further attack. The use of AI agents is evident for a number of reasons, most importantly:
- The shear volume of the attack and the number of artifacts generated, in a relative short period.
- The fact that attack scripts are commented and documented, and that the attack agents seem to be talking to each other int he comments of the scripts
Within minutes of the attack the first signals appeared in our monitoring system and an alert was sent to the volunteers of our SOC, for investigation.
Even tough the alert came quickly, it took us 19 hours to mount our first response on 22 Sept 2026, in this response we formulated a plan to contain the attack.
The execution of this plan took a further 9 hours. This included travel time to get the incident response team together at the Hermit Hive, our friendly hackerspace home away from home. And carefull movement to make sure that we where able to isolate our systems in the datacenter in Amsterdam, without isolating ourselves from the network and incapacitating further responses that where undoubtedly needed in the future.
Since then we have been investigating the incident to figure out what data is involveld. We have also communicated/reported this breach to our key partners, the Dutch Data Protection Authority, the Dutch Cyber Security Center (NCSCN-NL) and, via them, our regulating body under the Cyberweerbaarheidswet and filed a police report.
To give as much clarity as we can, we created an overview page that shows what data we have, the status of the investigation and which data is involved in the breach.
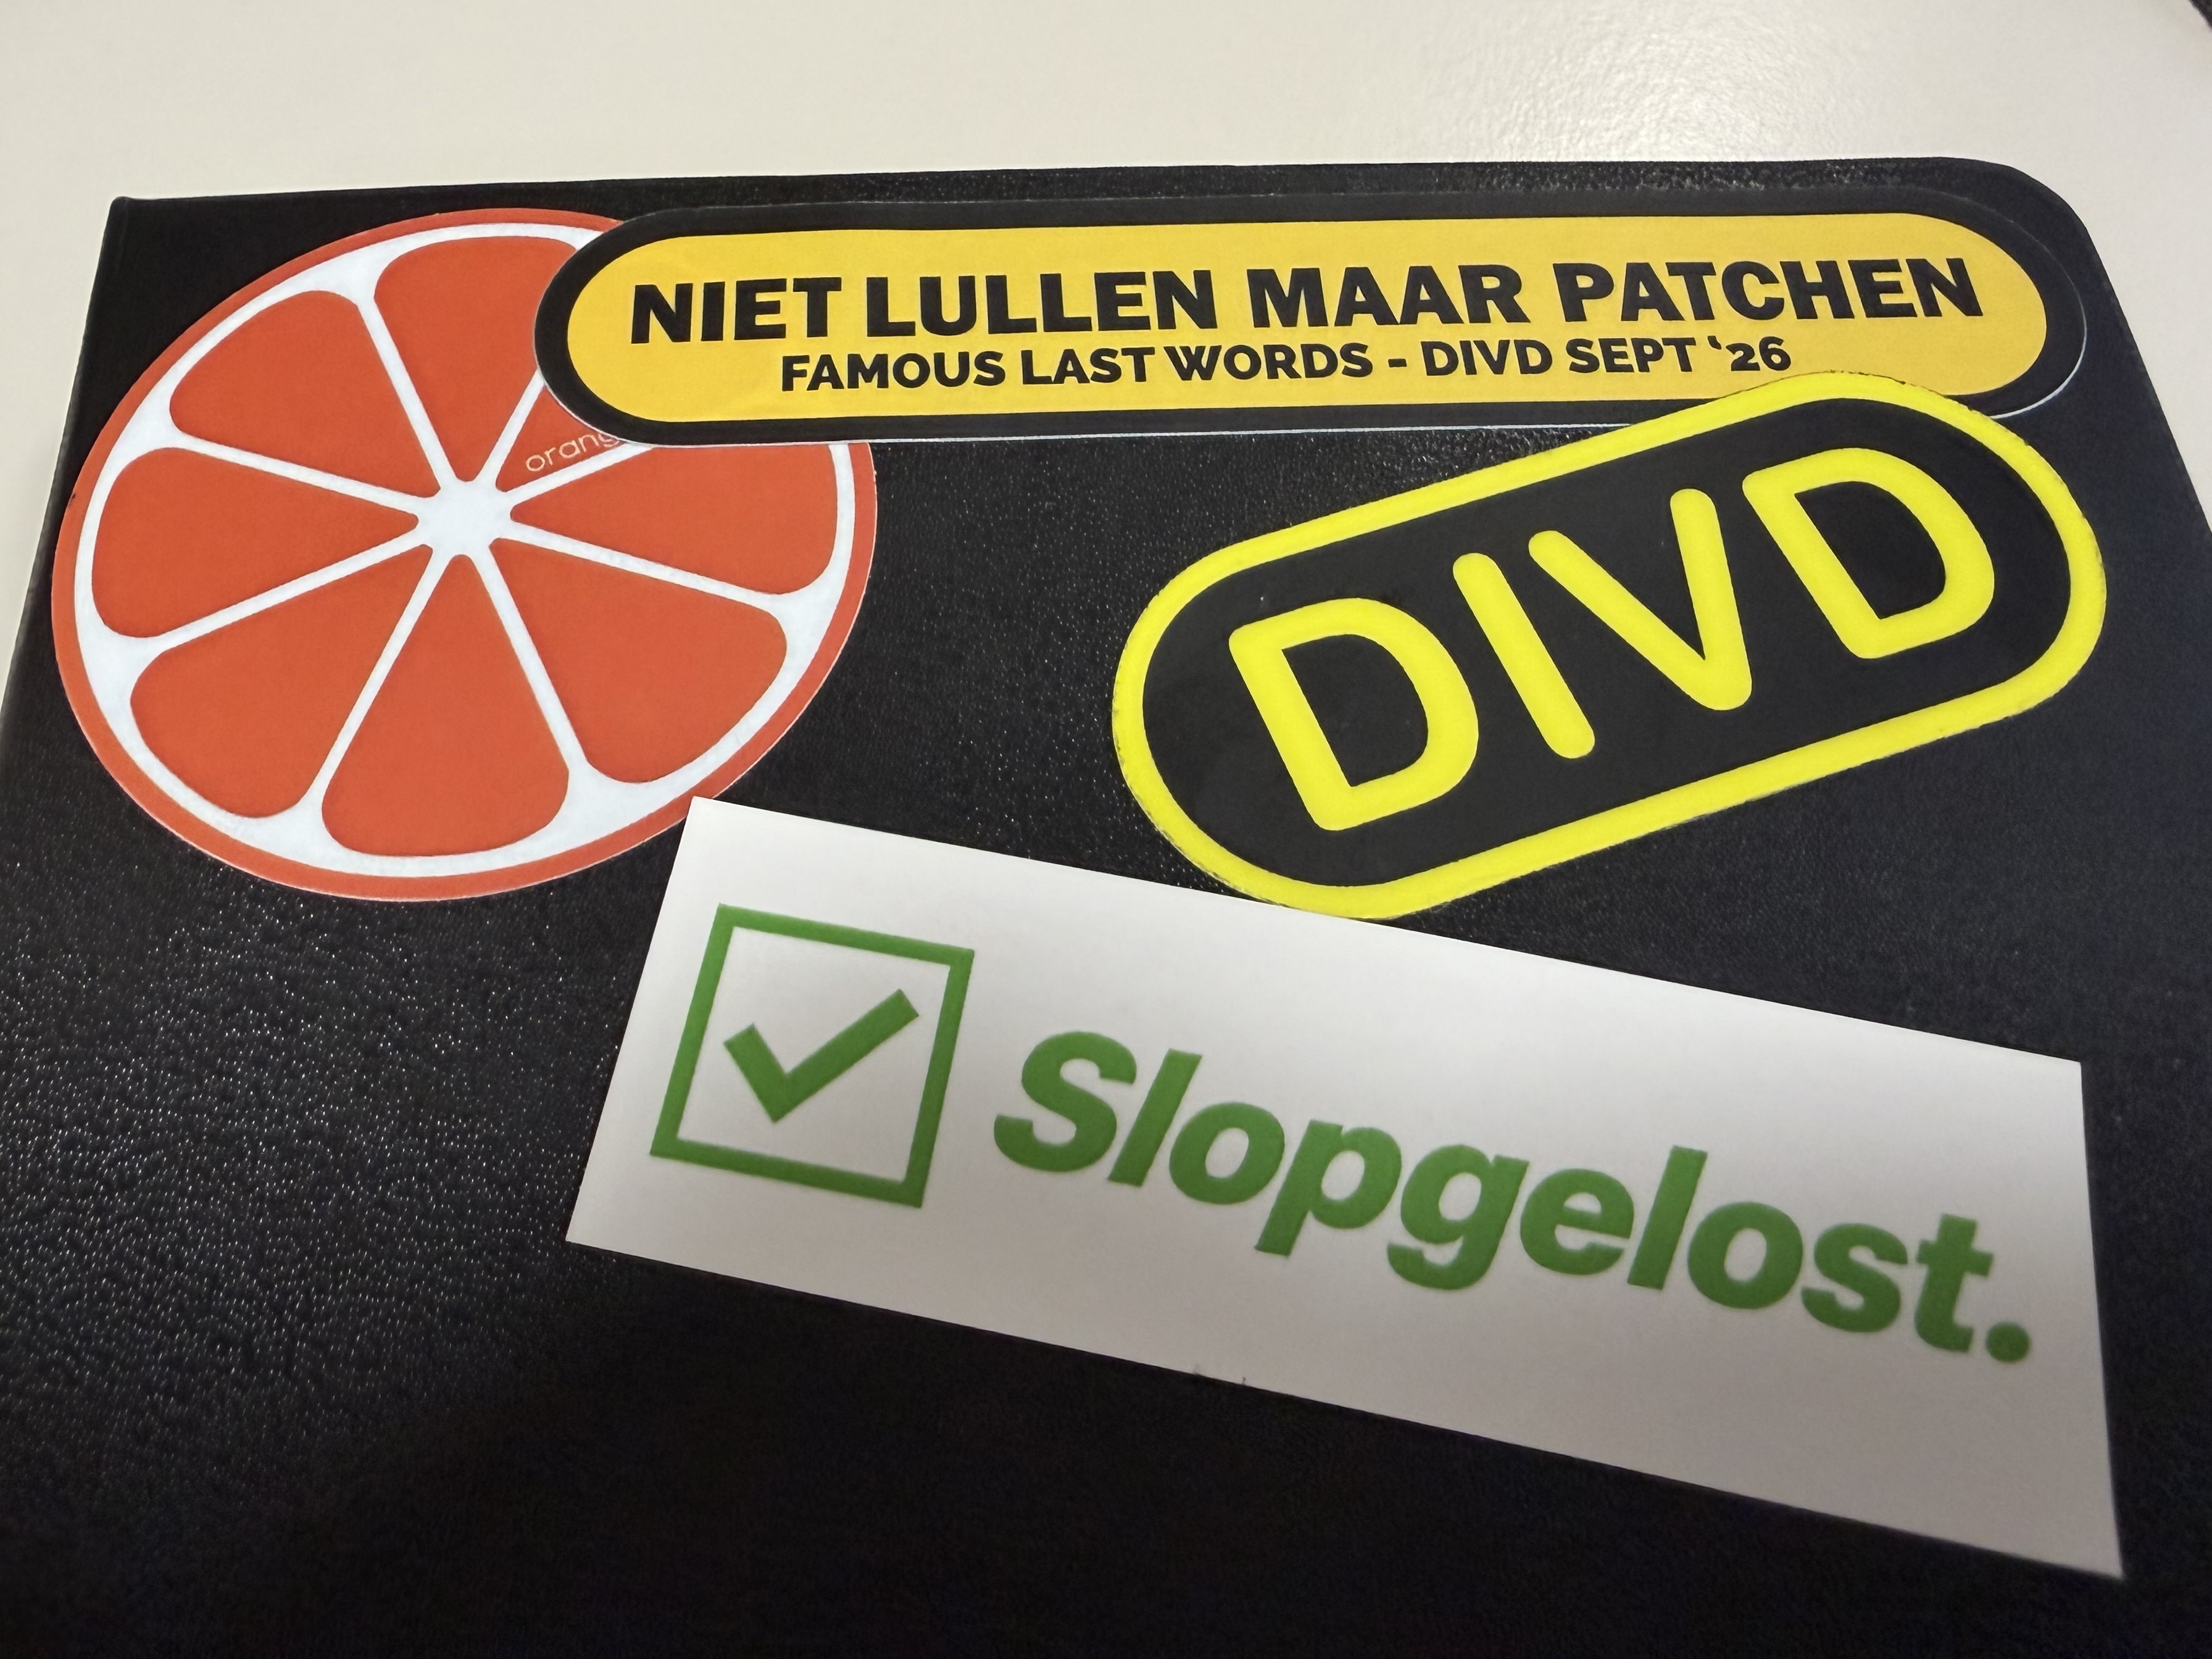
We wouldn’t be DIVD if we had not launched case DIVD-2026-00015 to warn other Zammad users who could fall victim to the same zero-days. And yes, since the Zammad 7.x branch was not vulnerable and we were not running it, we had special stickers made to remind ourselves to practice what we preach. Stop yapping, start patching.
Metrics
We are nerds. Nerds love metrics. Here are metrics.
| Mean Time to Detect (MTTD) | 19 minutes |
| Mean Time to Respond (MTTR) | 19 hours |
| Mean Time to Contain (MTTC) | 9 hours |
We said we love metrics, but perfectionists as we are, we see plenty of room for improvement. Then again, zooming out, these numbers are not too shabby compared to industry averages, let alone for a volunteer run organisation.
Public statements
We made na number of public statements about this hack on social media. So much we moved then to the public statements page.
More information
- Case DIVD-2026-00015 - The casefile for the 0-day vulnerabilities in Zammad
- Overview of the investigation into the status of our data
- Overview of public statements
We will update this page when we have more information.
Timeline
| Date | Description |
|---|---|
| 21 Sep 2026 | First access by malicious actor on DIVD systems |
| 22 Sep 2026 | DIVD becomes aware of malicious activity. Access to all systems in the datacenter is blocked |
| 22 Sep 2026 | Incident response team formed and forensic investigation started together with Merlon Security |
| 24 Sep 2026 | Vulnerability reported to Zammad. |
| 24 Sep 2026 | DIVD updated partners and affected parties. |
| 24 Sep 2026 | First public statement on LinkedIn about being hacked. |
| 26 Sep 2026 | DIVD started case DIVD-2026-00015, to scan for publicly available and vulnerable Zammad instances. |
| 26 Sep 2026 | DIVD created a limited disclosure for CVE-2026-102489 & CVE-2026-102490. |
| 26 Sep 2026 | Public statement on LinkedIn about the AI modus operandi. |
| 28 Sep 2026 | Public statement on LinkedIn about what we know so far. |
| 29 Sep 2026 | Publication of casefile |
| 30 Sep 2026 | Public statement on LinkedIn about zero-days in Zammad. |
| 30 Sep 2026 | DIVD informed partners and affected parties about data that might have been breached. |
| 01 Oct 2026 | Publication of overview of which data is compromised and which data is not. |
| 01 Oct 2026 | Public statement on LinkedIn about the data breach. |
| 05 Oct 2026 | Police report filed at 13:37 |
| 07 Oct 2026 | Presentation at the One Conference |
| 09 Oct 2026 | Case file overview of data investigation updated. |
Contact
If you want more information on our hack please reach out to All other questions can go to communications@divd.nl, if you are concerned about your PII please contact dpo@divd.nl